New: The Executive Guide to AI Readiness – Build the Operational Foundation for AI Success. Read Article

GRC Readiness Assessment

GRC Readiness Assessment & Consulting
Understand where your governance, risk, and compliance foundations stand — and where they need to be strengthened to support compliant execution, automation, and AI at scale.
GRC Assessment

About the GRC Readiness Assessment

The GRC Readiness Assessment helps leadership understand how governance, risk, and compliance practices operate across the enterprise and where gaps may affect execution, automation, and AI initiatives.
GRC Assessment Governance Risk Compliance
Why Assess

Why GRC Readiness Matters

Governance, risk, and compliance gaps don’t announce themselves — they accumulate quietly until they surface as audit failures, regulatory exposure, operational breakdowns, or barriers to scaling automation and AI. A GRC Readiness Assessment gives leadership a clear, structured view of where those gaps exist before they escalate.

Strong GRC readiness creates greater visibility into governance, risk, compliance, controls, evidence, and accountability. It helps organizations identify where foundations need to be strengthened before new capabilities are scaled.

Stronger GRC readiness means stronger enterprise execution.

Seven GRC Domains

What the Assessment Evaluates

The assessment evaluates seven GRC domains that collectively determine whether governance is strong enough to support compliant operations, automation, and AI at scale.
system

Governance Model

Evaluates whether decision rights, executive accountability, policies, and oversight are clearly defined and consistently applied across the enterprise.
assesment

Compliance & Controls

Evaluates whether policies are translated into defined, enforceable controls that are consistently executed, tested, and supported by evidence.
protocol

Security & Privacy

Evaluates whether safeguards for data, systems, vendors, and workflows are defined, enforced, and prepared for automation and AI-enabled environments.
risk

Risk Management

Evaluates how consistently enterprise risks are identified, assessed, owned, mitigated, and monitored across operations, data, vendors, automation, and AI.
logistics-management

Auditability & Evidence

Evaluates whether the organization can reliably demonstrate how decisions, controls, and workflows operate through accessible, durable, and traceable evidence.
integrations

AI Guardrails & Monitoring

Evaluates whether automation and AI operate within defined risk, quality, governance, monitoring, and human-oversight boundaries.
data

Operationalization & Scale

Evaluates whether governance, controls, and guardrails are embedded into repeatable execution and can remain effective as initiatives scale.
The Approach

Assessment Approach

The Full GRC Readiness Assessment is a structured, consultant-led evaluation grounded in stakeholder input and observable evidence. The assessment examines current GRC maturity across all seven GRC domains and translates findings into practical priorities.

01

Assess the current GRC posture across all seven GRC domains.

02

Evaluate stakeholder input and observable evidence to understand how governance operates in practice.

03

Identify domain-level maturity and priority gaps.

04

Recommend practical actions that strengthen governance, manage risk, and support future scale.
Maturity Scoring

GRC Maturity Presentation

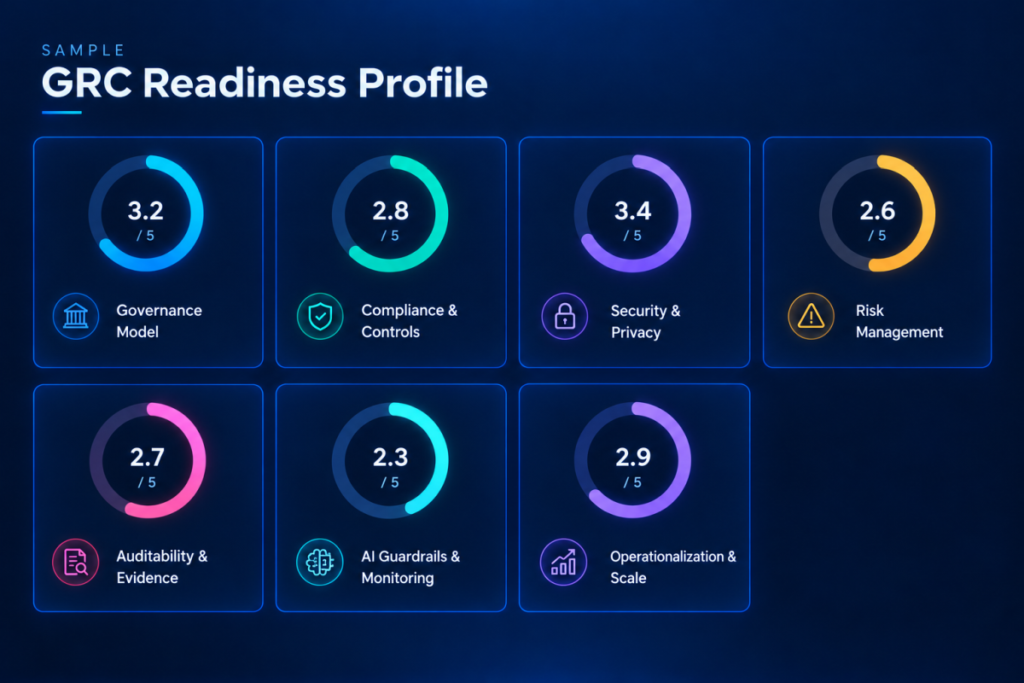
The Full GRC Readiness Assessment uses domain-level maturity scoring on a 1–5 scale. The seven domains stand on their own; scores are not tabulated into an overall GRC readiness score.

The GRC Readiness Overview is a focused, discussion-based review and should not be presented as a scored assessment unless scoring is separately confirmed.
Assessment Options

Choose Your Starting Point

Organizations can begin with a focused GRC Readiness Overview or proceed directly to the Full GRC Readiness Assessment, depending on the level of evaluation required.

GRC Readiness Overview

A focused, discussion-based review designed to help leadership explore current GRC challenges, identify potential areas of exposure, and determine whether a more comprehensive assessment is warranted. Best for: Organizations seeking an initial perspective on their GRC posture and where deeper evaluation may be valuable.

Full GRC Readiness Assessment

A structured, consultant-led assessment of current GRC maturity across Soltec’s seven domains, grounded in stakeholder input and observable evidence. Findings are translated into domain-level maturity insights, priority gaps, recommendations, and a practical improvement roadmap. Best for: Organizations seeking a comprehensive, evidence-based view of GRC maturity and clear priorities for strengthening governance, managing risk, and supporting future scale.

Deliverables

What You Receive

The Full GRC Readiness Assessment delivers clear, structured outputs — giving leadership the information and priorities needed to strengthen governance, reduce risk, and improve compliance posture.
Current-State Insights
A structured view of your current GRC posture across all seven domains — with domain-level maturity scoring.

Priority Gaps

Clear visibility into areas where governance, risk, compliance, controls, evidence, or operationalization may require attention.

Recommendations

Practical recommendations tied to identified findings and the organization’s current GRC posture.

Improvement Roadmap

A prioritized roadmap that translates assessment findings into practical next steps for strengthening GRC readiness.

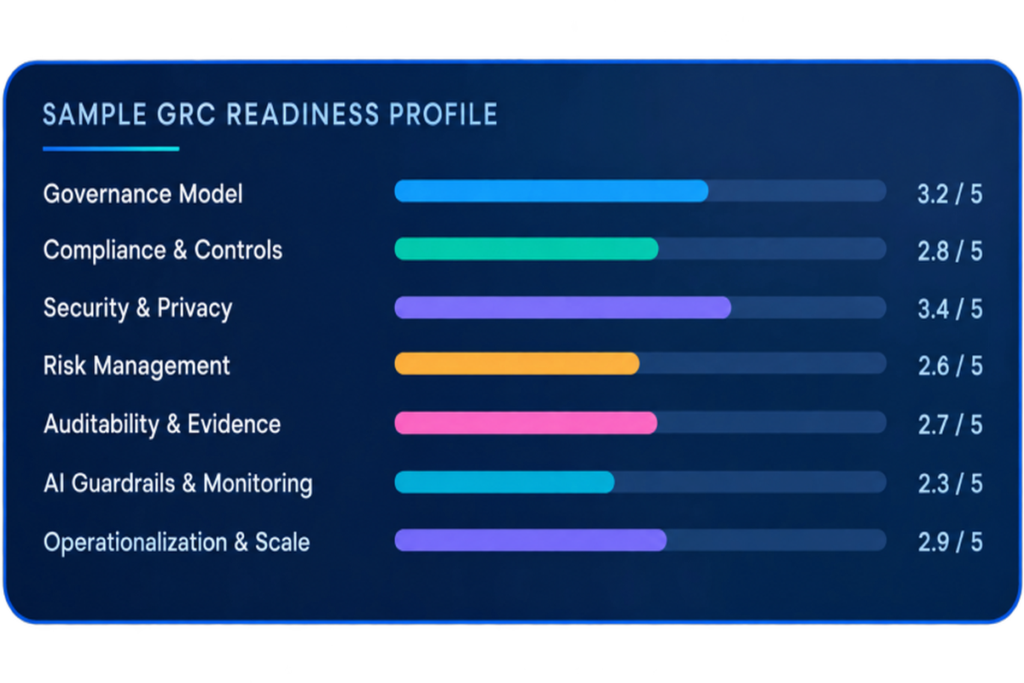
Sample Domain Maturity Profile

GRC DomainSample Maturity
Governance Model3.2 / 5
Compliance & Controls2.8 / 5
Security & Privacy3.4 / 5
Risk Management2.6 / 5
Auditability & Evidence2.7 / 5
AI Guardrails & Monitoring2.3 / 5
Operationalization & Scale2.9 / 5
Practical Roadmap

Outcomes You Can Expect

The assessment is the starting point — not the destination. Findings are translated into prioritized, practical recommendations and a clear improvement roadmap.
system

Stabilize Governance

Address foundational gaps in ownership, policies, controls, risk management, and evidence that may constrain what the organization can safely pursue.
data-quality (1)

Embed & Enforce

Strengthen governance by embedding controls into workflows, improving evidence capture, and establishing monitoring and accountability.
data

Operationalize & Scale

Extend governance consistently across processes, systems, automation, and AI so improvements can be sustained as the organization scales.

Strong GRC readiness creates the foundation for organizations to scale operations, automation, and AI with greater confidence.
Why Soltec

Why Enterprises Choose Soltec

Enterprise Consulting Experience

35+ years of enterprise consulting experience across complex, regulated, multi-industry environments.

We combine deep governance, risk, and compliance expertise with enterprise consulting and process design experience — giving organizations an assessment partner who understands how GRC works in practice, not just on paper.

Ready to understand your GRC readiness?

Get a clear view of your current GRC posture, identify priority gaps, and define practical next steps for stronger enterprise execution.

Frequently Asked

GRC readiness, answered straight.

The questions governance, risk, and compliance leaders ask before committing to an enterprise GRC program.
A GRC Readiness Assessment is a structured way to understand how governance, risk, and compliance practices operate across an organization, identify gaps, and define practical priorities for strengthening GRC readiness.
The assessment evaluates seven GRC domains: Governance Model; Compliance & Controls; Security & Privacy; Risk Management; Auditability & Evidence; AI Guardrails & Monitoring; and Operationalization & Scale.
The seven domains are Governance Model, Compliance & Controls, Security & Privacy, Risk Management, Auditability & Evidence, AI Guardrails & Monitoring, and Operationalization & Scale.
The Full GRC Readiness Assessment uses domain-level maturity scoring on a 1–5 scale. The seven domain scores stand on their own and are not combined into an overall GRC readiness score.
The GRC Readiness Overview is a focused, discussion-based review designed to help leadership identify potential GRC concerns and determine where deeper evaluation may be valuable. The Full GRC Readiness Assessment is a structured, consultant-led evaluation across Soltec’s seven GRC domains that produces maturity insights, identified gaps, prioritized recommendations, and an improvement roadmap.
The Full Assessment provides a structured view of the current GRC posture across all seven domains, domain-level maturity scoring, priority gaps, practical recommendations, and an improvement roadmap.
Strong GRC readiness helps organizations scale automation and AI with appropriate governance, controls, risk management, evidence, and oversight. Weaknesses in these areas can introduce risk or constrain how safely new capabilities can be deployed and scaled.
The assessment translates findings into prioritized recommendations and a practical improvement roadmap, with a progression from stabilizing governance to embedding and enforcing controls and then operationalizing and scaling governance across processes, systems, automation, and AI.
Scroll to Top